Onboard employees from LDAP
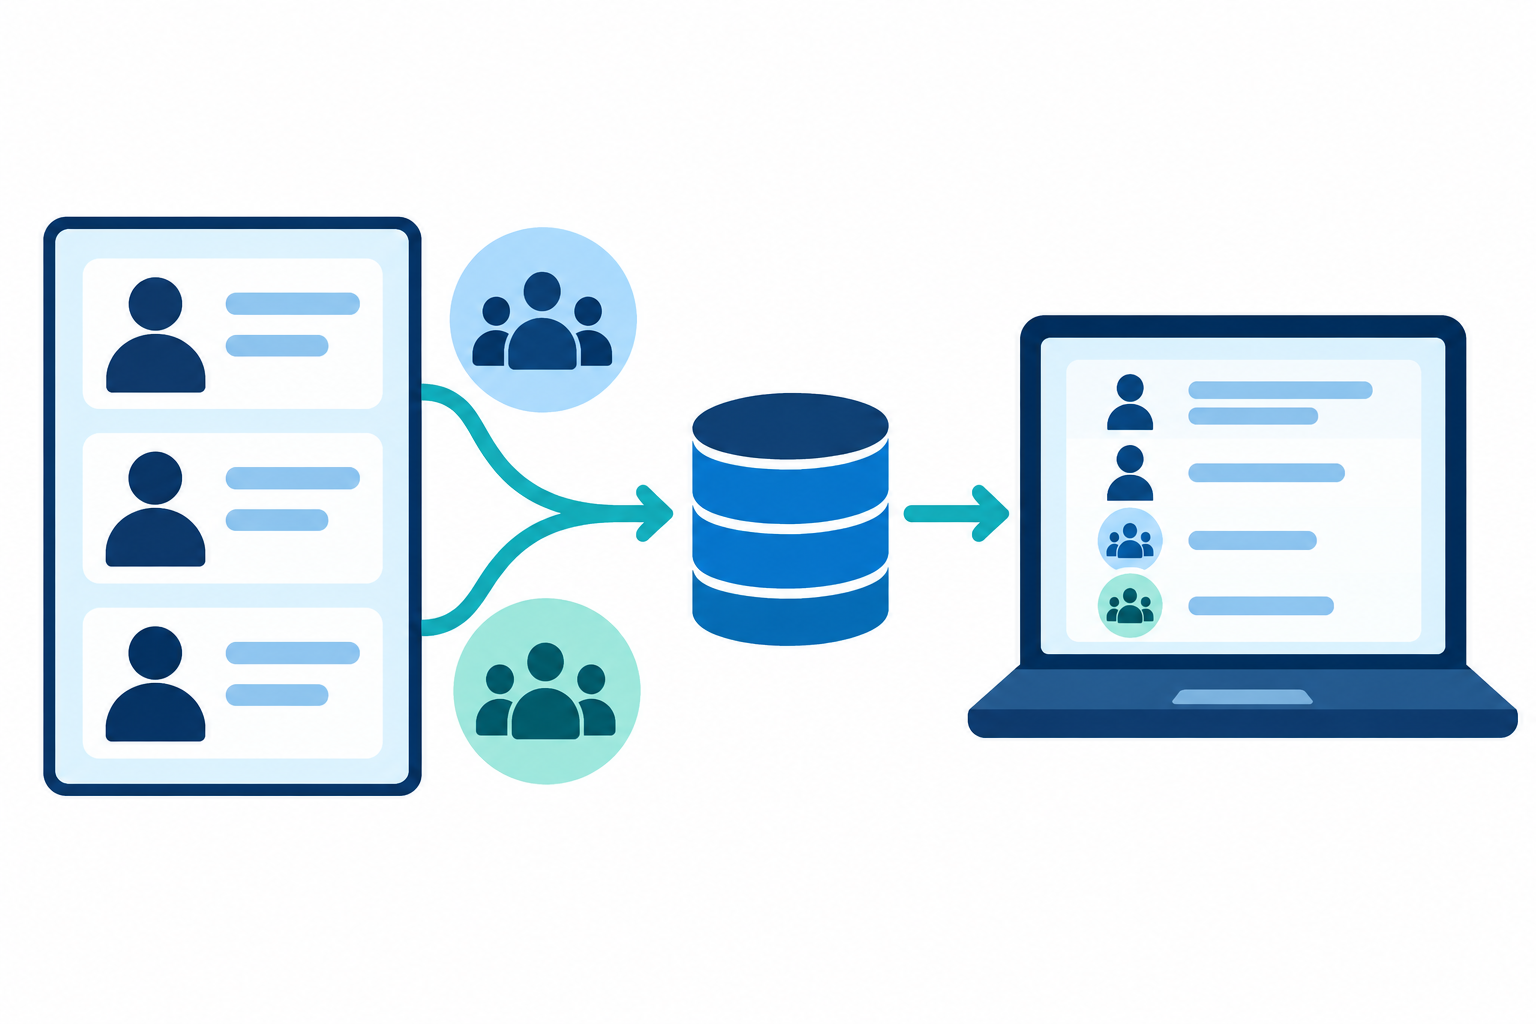
Goal: MDM contains up-to-date users and the selected directory groups.
Before you begin
Prepare a read-only bind account, access to the required branches, LDAPS, and a schedule with a time zone.
Procedure
- Configure LDAP and select groups.
- Check the user import.
- Check group membership.
- Assign work profiles to the MDM group.
Expected result
After synchronization, the membership of the selected group matches the directory; the profile assignment is verified separately.
If the result differs
A successful bind does not prove that the import worked. LDAP membership is changed in the source directory, not in the synchronized MDM group.
Changes and rollback
Confirm the recipients before changing an assignment. Test the new value on a test device first. Do not treat removing an assignment as an automatically confirmed rollback of all local settings: check the final state of the device and the application.
Last updated